A 3-Step Security Review for AI-Built Apps Before Launch
A practical first-pass review for database authorization, server-side credentials, and unauthenticated exposure before an AI-built application reaches real users.
 Access boundary audit
Decision brief
The short answer
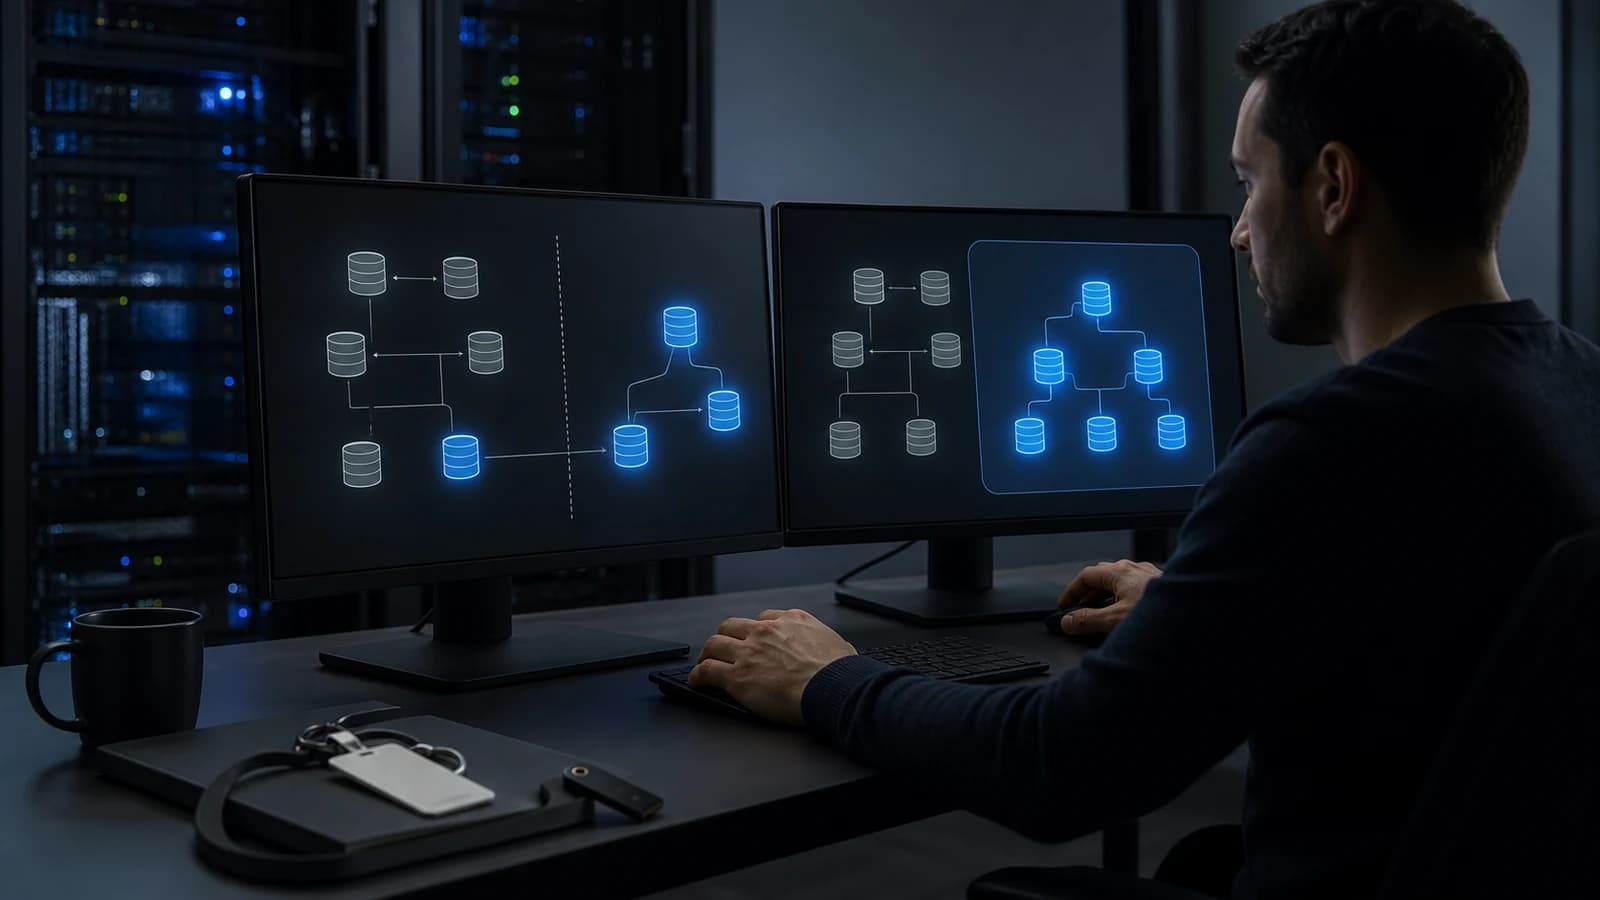
Before launch, prove three boundaries: users cannot read or change another user's data, privileged credentials never reach the browser, and sensitive actions fail closed when identity or authorization is missing. A polished interface is not evidence that any of those controls work.
Run protected reads and writes as the wrong user and as an unauthenticated visitor.
Inspect the deployed browser bundle and network calls for privileged credentials.
Turn every failed check into a repeatable test that blocks release.
At a glance
What to carry into the decision
- Test every protected data operation as the wrong user, not only as the intended user.
- Keep privileged credentials and irreversible actions behind a trusted server boundary.
- Record failed access checks as launch blockers with owners and repeatable verification steps.
Key Takeaway
Before launch, test the database authorization boundary, confirm that private credentials remain in trusted server code, and verify that unauthenticated requests cannot reach protected data or actions. These checks are a first pass, not a complete security assessment.
AI-assisted tools can shorten the path from a product description to a working prototype. That speed is useful, but it does not establish whether the deployed application protects user data and privileged actions.
Generated implementations vary with the prompt, selected integrations, platform defaults, and later edits. Security therefore needs to be tested as behavior, not inferred from the tool that produced the code.
Two high-impact failure classes are missing record-level authorization and private credentials shipped to the browser. Either can expose data or allow unauthorized use of paid and privileged services.
You can run a useful first-pass review without a full security team. These three checks surface common authorization and credential failures, but higher-risk products still need a threat model and deeper testing appropriate to their data and users.
Step 1: Enforce Database Authorization
If your app uses a backend-as-a-service such as Supabase or Firebase, browser clients may communicate directly with managed data APIs. This is convenient, but every data path still needs explicit authorization.
Supabase uses PostgreSQL Row-Level Security (RLS) policies. Firebase uses Security Rules. The names and syntax differ, but the requirement is the same: a user must only be able to perform operations permitted for their identity and role.
The Audit:
- Open your data-platform dashboard and identify every collection, table, storage bucket, and callable endpoint exposed to a client.
- For Supabase, inspect RLS enablement and policies. For Firebase, inspect Firestore, Realtime Database, and Storage Security Rules.
- Test authenticated and unauthenticated access against each sensitive operation.
The Fix:
For Supabase, enable RLS on exposed tables and write policies that define who can access each row. For example, a basic policy for a profiles table would look like:
-- Allow users to read and update only their own profile
create policy "Users can modify own profile"
on profiles for all
using (auth.uid() = id);
If you aren't sure how to write the SQL policy, ask your AI developer: *"Write a Supabase RLS policy for my 'tasks' table so that users can only read, create, update, or delete tasks where user_id matches their authenticated user ID."*
Step 2: Hide Your API Keys Behind Server-Side Endpoints
Many AI-built MVPs call external services like OpenAI, Stripe, or SendGrid directly from the browser.
Generated code can accidentally place a private API key in a browser bundle. Browser-delivered JavaScript, network requests, and embedded configuration can be inspected by users, so a credential exposed there must be treated as compromised and rotated.
The Audit:
- Search your frontend code for terms like
sk_(Stripe secret keys),sk-proj-(OpenAI keys), or other developer credentials. - If you find these keys in any file that runs in the browser (like a React page or component), you have a security leak.
The Fix:
Never call credential-heavy APIs directly from the browser. Instead, use a backend helper (like a Next.js API Route, Server Action, or Supabase Edge Function).
- Store your API keys in environment variables (
.envfile) on your hosting provider (like Vercel or Supabase). - Create a secure API route on your backend.
- Have your frontend call your *own* API route, and let your backend make the call to OpenAI or Stripe using the hidden environment variable.
For example, in Next.js, instead of calling OpenAI on the frontend, create an API route:
// app/api/chat/route.ts
import { NextResponse } from 'next/server';

export async function POST(req: Request) {
  const { prompt } = await req.json();
  const apiKey = process.env.OPENAI_API_KEY; // Securely stored on the server

  const response = await fetch('https://api.openai.com/v1/chat/completions', {
    method: 'POST',
    headers: {
      'Content-Type': 'application/json',
      'Authorization': `Bearer ${apiKey}`,
    },
    body: JSON.stringify({
      model: process.env.OPENAI_MODEL,
      messages: [{ role: 'user', content: prompt }],
    }),
  });

  const data = await response.json();
  return NextResponse.json(data);
}
Step 3: Run an Unauthenticated Exposure Check
This narrow check verifies that common unauthenticated paths reject access. It is useful, but it is not a penetration test and does not replace a scoped professional security assessment.
The Audit:
- Open an Incognito Window: Do not log in to your app.
- Access Private URLs: Try to visit dashboard routes directly (e.g.,
https://yourapp.com/dashboard). Does the app redirect you to log in, or does it show empty components and leak interface elements? - Inspect the Network Tab: Open your browser's Developer Tools (F12 or right-click -> Inspect), go to the Network tab, and reload your page. Look at the API requests being made. Click on them and read the response. Can you see data that shouldn't be visible to a logged-out guest?
- Try to Modify Data: If you have command-line experience, try sending a
POSTorPATCHrequest to your database endpoint using a tool like Postman orcurl, without passing an authentication token. Does the server reject the request with a401 Unauthorizedor403 Forbiddenstatus code?
The Launch-Ready Security Checklist
Before you post your MVP on Product Hunt or Twitter, verify you've checked these three boxes:
- [ ] Data authorization: Every table, bucket, or endpoint exposed through a client-accessible API has explicit and tested access rules.
- [ ] Secret management: No private API keys (keys starting with
sk_,key_, etc.) exist in the frontend code. - [ ] Server enforcement: Protected reads, writes, and actions reject unauthenticated or unauthorized requests even when the interface is bypassed.
Turn Security Findings into Launch Blockers
Turn each failed check into a launch blocker with an owner, a corrective change, and a repeatable verification step. This creates evidence that the boundary was tested and helps prevent the same class of failure from returning.
If you have built an MVP using AI but feel unsure about database rules, server-side functions, or API routes, ZamDev AI can help.
Our codebase audit returns reproducible findings, risk-ranked remediation, and written acceptance criteria. It does not replace a penetration test or compliance review when the product risk requires one.
Evidence and scope
What this guide is based on
The checks are a practical first-pass review, not a substitute for a threat model, penetration test, or compliance assessment appropriate to the product's risk.
Intended for: Founders and product teams preparing an AI-built application for real users.
Frequently Asked Questions
Why are AI-built applications vulnerable to database leaks?+
How do I secure private API keys in a frontend framework?+
What is the fastest way to test if my database is secure?+
Related Articles
Written by
Zamad Shakeel
Founder & CEO, ZamDev AI · Full-Stack Engineer & AI Systems Builder
Zamad designs and ships AI products, agentic workflows, enterprise automations, and the production controls that make those systems dependable after launch.
linkedin.com/in/zamad-gopang →Turn the decision into a working system.
ZamDev AI helps teams design and deliver AI products, connected automations, knowledge systems, and production improvements with a clear scope and measurable acceptance criteria.
Or WhatsApp us directly: +92 328 635 6880