Technical Due Diligence for AI Startups: A Preparation Checklist
Technical due diligence varies by investor and company stage. This checklist helps founders prepare evidence about security, tests, deployment, architecture, ownership, and AI-provider risk without promising an investment outcome.
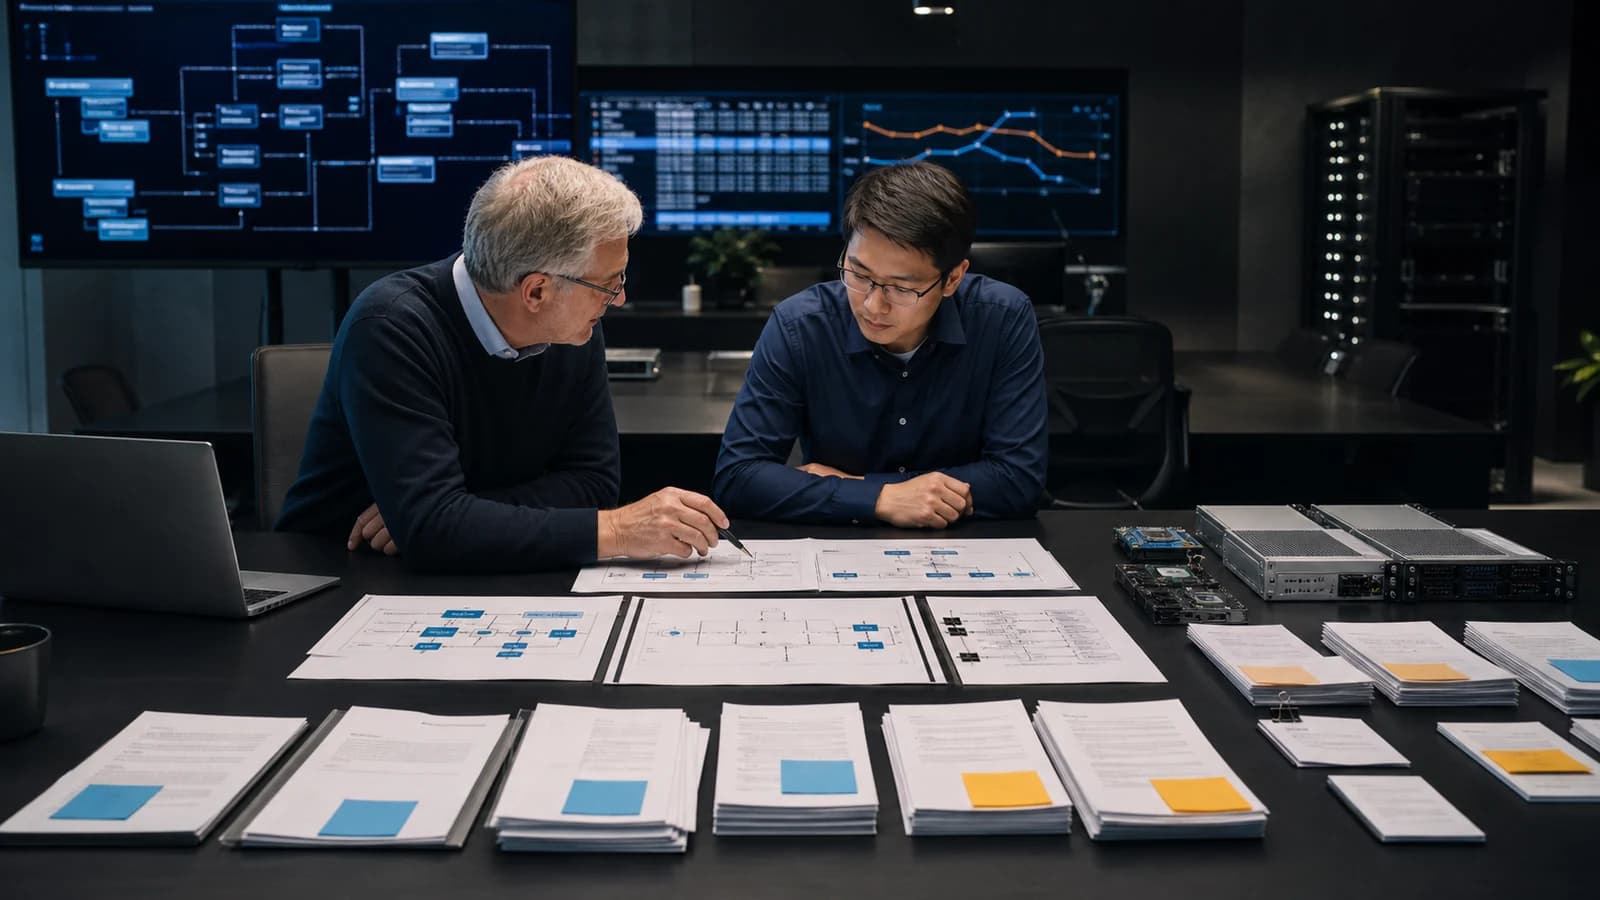 Diligence evidence room
Decision brief
The short answer
Prepare a reproducible evidence room that shows how the product is built, tested, deployed, secured, measured, and recovered. Reviewers need enough evidence to distinguish a known, owned risk from an unknown dependency or an unsupported architecture claim.
Link claims to code, test results, configuration, incident records, or operating dashboards.
Document model and data dependencies, evaluation methods, access boundaries, and material limitations.
Assign each accepted risk an owner, decision, and follow-up date.
At a glance
What to carry into the decision
- Prepare reproducible evidence, not only architecture diagrams and verbal assurances.
- Document access boundaries, test gates, deployment ownership, incidents, dependencies, and AI evaluation.
- Resolve critical unknowns early and label accepted risks with owners and follow-up dates.
Key Takeaway
A technical reviewer may examine security boundaries, software ownership, test evidence, deployment controls, architecture risks, data governance, and AI-provider dependencies. Ask for the actual diligence scope, answer with evidence, and distinguish current controls from planned work.
Congratulations - you've passed the pitch stage. The investor is interested. Now they want to do technical due diligence.
An effective demo does not answer questions about data access, intellectual-property ownership, operating risk, or maintainability. A repository review may surface material issues that require remediation, disclosure, or a revised technical plan.
The exact review depends on the investor, stage, product, regulated obligations, and transaction. Use the following sections as preparation prompts, not a claim about every investor.
1. Security Hygiene and Data Boundaries
A reviewer may start with obvious, high-impact security failures because they are relatively quick to verify and can affect users, contractual obligations, and operating risk.
What They Check
- Exposed API keys: Searching the repository for strings like
sk-,sk_live_,OPENAI_API_KEYin committed code - Missing database authorization: Checking whether sensitive Supabase tables have appropriate Row-Level Security policies and whether equivalent controls exist on other platforms
- Public data endpoints: Testing if unauthenticated API calls can access user data
- Secrets in environment examples: Checking
.env.examplefor real values
How to Pass
Run this command in your repository to find any accidental key exposure:
git log --all --full-history -- '*.env*'
git grep -r "sk-proj|sk_live|AIza" .
If anything appears, use git filter-repo to remove it from history and immediately rotate the exposed key.
2. Test Coverage: The Trust Signal
The absence of meaningful tests makes it harder to demonstrate that critical behavior is repeatable and that changes can be reviewed safely. Test count or coverage percentage alone is not proof; reviewers care about whether important risks and workflows are exercised.
What They Measure
- Do the tests assert meaningful behavior instead of only rendering components or using placeholder cases?
- Does the CI pipeline run tests on every pull request?
- Are there tests for the most critical paths: user authentication, payment processing, and data writes?
The Minimum Viable Test Suite
You do not need a universal coverage target. Start with the paths whose silent failure would interrupt revenue, access, customer data, or core operations:
// Example: Critical path test for checkout flow (Playwright)
test('user can complete checkout', async ({ page }) => {
  await page.goto('/pricing')
  await page.click('[data-testid="plan-starter"]')
  await page.fill('[name="email"]', 'test@example.com')
  // ... complete the flow
  await expect(page.locator('[data-testid="success-message"]')).toBeVisible()
})
A small risk-based suite covering critical behavior can be more informative than a large set of low-value tests.
3. Deployment Pipeline: The Maturity Signal
How you deploy tells investors how mature your engineering process is. A thoughtful deployment pipeline signals that you take reliability seriously.
Evidence to Prepare
- A CI/CD pipeline (GitHub Actions, Vercel) that runs automatically on every commit
- Separate staging and production environments
- Environment variables managed through platform secrets (not hardcoded)
- Database migrations checked into version control
Questions to Resolve
- Who can deploy, and what review or rollback control applies?
- Where are changes tested before production, and how are environment differences managed?
- Are database changes reproducible from versioned migrations?
- Are secrets excluded from the repository and managed through controlled platform settings?
4. Architecture Scalability: The "What Happens at 10x?" Question
A reviewer may assess whether the architecture can support the operating plan and whether known limits are measured and documented.
What They're Really Asking
If your app gets 10x more users next year, what breaks? A good answer shows you've thought about this. A concerning answer is "I'm not sure."
The Key Questions to Prepare For
- Database: How are connections, query plans, tenancy, backup, and recovery handled as usage grows?
- AI costs: How does provider usage scale, which requests can be cached safely, and where are budgets and alerts enforced?
- File storage: Where do uploads go, who can access them, how are retention and malware risks handled, and what limits apply?
Prepare a simple architecture diagram showing data flow through your system. Even a basic one shows technical awareness.
5. AI Dependency and Evaluation Risk
A reviewer may ask: "What happens to the product if a model provider changes pricing, availability, policy, regional support, or model behavior?"
The Concern
Many AI startups are built as thin wrappers around a single model. If provider pricing changes, availability drops, or a relied-on behavior shifts in a model update, the entire product can be affected.
How to Show You've Thought About This
- Dependency boundary: Keep provider-specific code behind a narrow interface when switching or fallback is a material requirement
- Evaluation evidence: Show representative tests for quality, tool use, safety, latency, and failure behavior
- Fallback handling: Document what happens when the provider is unavailable, including whether the correct response is a retry, queue, human review, alternate provider, or explicit failure
// Keep provider access behind a narrow, policy-aware boundary.
async function generateSummary(
  documentId: string,
  accessContext: AccessContext,
): Promise<SummaryResult> {
  try {
    const summary = await approvedProvider.summarize({ documentId, accessContext })
    return { status: 'ok', summary }
  } catch (error) {
    if (isRetryable(error)) {
      await queueForRetry({ documentId, policyVersion })
      return { status: 'queued' }
    }
    return { status: 'unavailable' }
  }
}
The Pre-Due-Diligence Cleanup Checklist
Before a technical review, adapt this list to the requested diligence scope:
- [ ] Security: Secret scans and history review are complete; sensitive data paths have appropriate authorization and negative tests
- [ ] Ownership: Code, data, accounts, dependencies, licenses, and contributor rights are documented
- [ ] Tests: Critical business, authorization, billing, migration, and recovery risks have meaningful automated or reproducible checks
- [ ] Delivery controls: Review, CI, deployment permissions, migration, rollback, and incident ownership are documented
- [ ] Architecture evidence: A current diagram shows trust boundaries, data flow, providers, and material operating limits
- [ ] AI evaluation: Model calls, permissions, datasets, quality measures, fallback behavior, and provider dependencies are documented
- [ ] Environment strategy: Production changes can be verified safely without using live customer data as a test fixture
If you are approaching a funding round, request a codebase risk review and share the diligence scope you need to prepare for.
We can review the agreed code, security boundaries, tests, deployment process, and technical documentation, then return reproducible findings and a prioritized remediation plan. That work can improve the quality of your technical evidence; it cannot guarantee an investment or diligence outcome.
Evidence and scope
What this guide is based on
This is a technical preparation guide, not legal, financial, or investment advice. Diligence requirements vary by transaction, product risk, and reviewer.
Intended for: AI startup founders preparing technical evidence for investors, acquirers, or enterprise buyers.
Frequently Asked Questions
What do VCs actually look at during technical due diligence?+
How long does it take to fix a codebase before a technical due diligence review?+
Does an AI-built app hurt my chances of raising funding?+
Related Articles
Written by
Zamad Shakeel
Founder & CEO, ZamDev AI · Full-Stack Engineer & AI Systems Builder
Zamad designs and ships AI products, agentic workflows, enterprise automations, and the production controls that make those systems dependable after launch.
linkedin.com/in/zamad-gopang →Turn the decision into a working system.
ZamDev AI helps teams design and deliver AI products, connected automations, knowledge systems, and production improvements with a clear scope and measurable acceptance criteria.
Or WhatsApp us directly: +92 328 635 6880